

 10 hours ago
5
PROTECT YOUR DNA WITH QUANTUM TECHNOLOGY
Orgo-Life the new way to the future Advertising by AdpathwayThere have been "millions" of exploitation attempts since a "critical" security flaw affecting websites around the world emerged, according to a major tech company.
A number of government and business websites went offline on Wednesday as a security measure after an urgent software update was issued over vulnerabilities in PHP, a programming language used extensively across the internet.
The developers of PHP said that a set of new updates fixing two previously identified critical vulnerabilities was now live, and strongly encouraged users to update software immediately.
Cloudflare CEO Matthew Prince wrote on X: "In the 10 hours before it was publicly announced, across the network we saw thousands of attempts to exploit it. That jumped to tens of thousands in the 45 minutes post announcement, hundreds of thousands within two hours, and millions now."
Amazon Web Services also said this flaw is now "being broadly exploited in the wild" - and has revealed that suspected hackers tried to capitalise on the vulnerability days before it was publicly announced.
Why websites across Europe went dark and what happens next?
This comes after an expert told Sky News that disruption will likely become "more widespread" as opportunistic hackers attempt to strike companies trying to patch the fault.
Cyber security officials have said that those unable to apply the fixes should consider temporarily taking their websites down.
Alp Toker, a cyber security expert and director at NetBlocks, called the issue "highly impactful" - and warned the disruption caused by nefarious actors, which has so far been "limited", could become "more widespread".
Speaking to Matt Barbet on The World, Mr Toker explained that the incident "means that anybody on the web can essentially access your web server if you're running the [PHP] software".
He said that the risk had been "very limited because the people who found the vulnerability kept it under wraps for quite a while, but in the last few days it has been seen in the wild".
Mr Toker added that AI agents could "reproduce the attack much more easily", warning that it is "just the beginning of a wider wave of attacks".
"These systems are going to continue to get compromised - month after month, year after year," he said.
'Critical security issues'
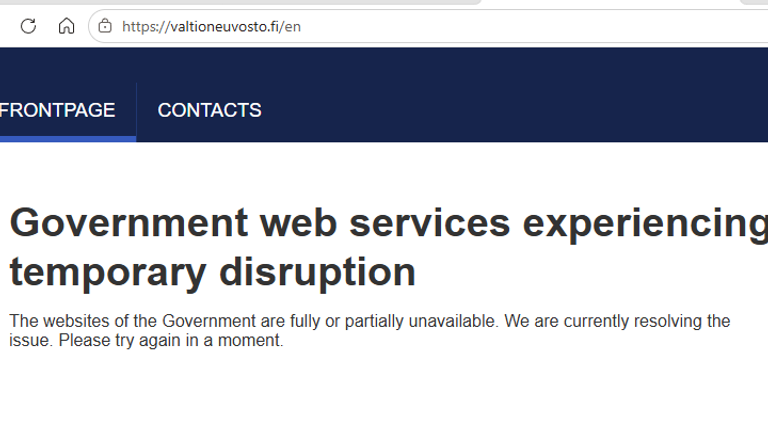
Websites linked to governments across Europe went offline on Wednesday as organisations rushed to protect their systems, although some are now back up and running.
In the UK, the Office for Budget Responsibility (OBR) said it had taken its website offline "in view of the critical security issues affecting PHP".
Oxfordshire County Council and Hillingdon Council both separately said they had temporarily taken down their websites as a precaution while they investigate.
A UK government spokesperson said work was under way to "identify and patch any potential exposure".
They added: "We encourage all organisations - private and public, large and small - to follow guidance issued by the NCSC to understand their exposure and take the necessary actions to safeguard their systems."
Meanwhile, the US National Security Agency and the Australian Cyber Security Centre both urged organisations to remain vigilant and apply updates where possible.
The Wikimedia Foundation, which runs online encyclopaedia Wikipedia, was one company on Wednesday that said it was in the process of addressing security vulnerabilities in the PHP programming language.
More from Sky News:
Why is Poland reopening Cold War bunkers?
Law must be updated to protect 'backbone' of UK
How was the rest of Europe affected?
- Belgium: The foreign ministry said it had temporarily taken its website offline, although the country's cybersecurity centre said there had been no attacks on Belgian websites
- Czech Republic: The government said its website was taken down to "allow for the implementation of necessary security patches". It said that "services will be restored once the recommended security updates have been applied"
- Finland: The government's public web services were shut down by the state IT centre Valtori as "a precautionary measure", adding that the outage was not the result of a data breach
- France: The websites of local government administrative offices were temporarily taken down as a precaution, the interior ministry said
- Germany: The country's digital ministry said that the federal IT service provider ITZBund had taken several websites offline but insisted no security incidents were known to have occurred
- Netherlands: A number of organisations took their sites offline, including the government site Overheid.nl, the Port of Rotterdam, the national football association KNVB, and the websites of the country's five largest political parties
PHP widely used
PHP is used by almost 70% of websites, according to cyber security firm Cloudflare, and underpins popular platforms such as WordPress and Magento.
It said the two vulnerabilities found, which AI agents helped to uncover, were rated 9.2 out of 10 on the CVSS v4.0 severity scale.
OpenAI, which runs ChatGPT, said it has been leading a team of researchers to address the flaw in PHP over the past two months - and supported its developers as it led the fixes.
The company called the incident "one of the most impactful security issues in recent memory", adding that while AI can help to uncover issues, it can also aid attackers.
On Tuesday, the European Union Computer Emergency Response Team (CERT-EU) said the 9.2 rating indicated a risk of unauthenticated remote code execution, a type of flaw that could allow attackers to run malicious code on vulnerable systems without logging in.
It urged organisations to prepare for the immediate patching of affected assets.




.png)

.jpg)

 English (US) ·
 French (CA) ·